Digital Health Company Insurance
The Coverage Gap That Turns One Claim Into a Company-Ending Event
Index

Gordon B. Coyle
CEO, The Coyle Group
845-474-2924
How to get started
Key takeaways
If you run a digital health company, insurance probably feels like a box a hospital or an investor forces you to check.
Then someone on your team says HIPAA questions are starting to block deals, and suddenly insurance is not a box anymore. It is a blocker.
Here is the problem underneath all of it. A digital health company is neither a pure software company nor a traditional medical practice.
It is both at once, and standard policies are written for one or the other. Your telehealth platform, your app, your remote monitoring tool, your AI clinical support, your wearable: each one creates technology risk and clinical risk at the same time, often across two separate legal entities.
That is exactly the seam where digital health company insurance either holds or fails.
Getting it right is the difference between a claim that gets paid and a claim that ends the company.
The Coyle Group is a commercial insurance agency that handles the complex, high-value risks other agencies don’t know how to structure, where the details in the policy are the difference between a paid claim and a denied one.
From what I’ve seen over 40 years, digital health is one of the easiest places in the entire market to get this wrong.
You are here because generic coverage does not fit a company that sits between healthcare and technology.
Most digital health founders buy a cheap startup package, assume “cyber covers the software” and “malpractice covers the platform,” and never find the gap until a claim falls straight into it. We build the program around what your company actually does, which entity carries which risk, and what your contracts and investors require, so nothing important lands in the space between policies.
Want a straight answer on where your gaps are? Book a call with Gordon.
Why is insurance for a digital health company so confusing?
It is confusing because your company creates two different kinds of risk that live in two different insurance worlds, and no single off-the-shelf policy was built to cover both. That is the trap. A doctor’s office with just 5,000 patient records breached is looking at north of $700,000 in response costs, and roughly 60% of small and mid-sized businesses fail following a serious cyber event. When the wrong policy answers that claim, the number does not shrink. It just becomes yours. Healthcare has been the most expensive industry in the world for a data breach for more than a decade running, according to IBM’s Cost of a Data Breach research.
Frankly, most founders assume Tech E&O, cyber, and medical malpractice are basically the same thing with different labels. They are not.
Each one triggers a different policy, and each of those policies typically excludes the others.
In my experience, that is why so many digital health company insurance programs look complete on paper and collapse the first time a real claim tests them.
This is the deeper reason I built The Coyle Group to work differently.
Business owners deserve a program built from the ground up for their actual exposures, not a template copied from whatever the last broker sold them.
Not sure whether your current policy would even respond to your most likely claim? Contact our team and we will read it with you.
What is a digital health company, and why does its risk look different?
A digital health company is any business using technology to deliver, support, or improve healthcare: telehealth platforms, health and wellness apps, remote patient monitoring, clinical decision support and AI tools, SaaS built for providers, and connected devices. Its risk looks different because the moment software touches patient care, technology failure and patient harm become the same event, and that changes everything about coverage.
That is the core distinction I want you to hold onto, because it drives every decision below.
I call it the difference between platform risk and clinical risk.
A traditional technology firm insurance program is built for platform risk.
A medical malpractice program is built for clinical risk.
Your company generates both, frequently through two entities: a technology company that runs the platform and a separate professional corporation that employs or contracts the clinicians.
Here is how those business models map to their primary exposures.
Your business model |
Primary exposures |
Coverage center of gravity |
|---|---|---|
|
Pure SaaS / analytics for providers |
Software failure, data/PHI, contract liability |
Tech E&O + Cyber |
|
Telehealth with clinicians |
Patient harm, PHI, software failure |
Medical Professional Liability + Cyber + Tech E&O |
|
Clinical decision support / AI |
Wrong or missed recommendation, patient harm |
Tech E&O (clinical wording) + Med Mal + Cyber |
|
Remote monitoring / wearables / devices |
Device failure, bodily injury, PHI |
Product Liability + Tech E&O + Cyber |
|
Pharmacy / billing / RCM |
Regulatory, billing audits, PHI |
Cyber + Regulatory + Tech E&O |
Over 40 years I’ve found that when a founder can see their model in a grid like this, the whole “what do I even need” fog lifts fast.
Want us to map your specific model to the right coverage center of gravity? Book a call.
What insurance does a digital health company actually need?
At minimum, a digital health company needs Technology E&O, Cyber and privacy, and, if any clinical care is involved, Medical Professional Liability, layered on top of General Liability, and usually Directors and Officers once you take outside money. The exact stack for digital health company insurance depends on your model, but the confusing part is not the list. It is knowing which policy pays which claim.
Here is the working stack, with the trigger for each:
Not every company needs every layer.
If you are a pure analytics tool that only touches de-identified data, employs no clinicians, and never influences a clinical decision, you can often skip Medical Professional Liability and run a lighter program, though Tech E&O and cyber still apply.
If your model is closer to pure software, the shape looks a lot like SaaS insurance with a heavier privacy and clinical overlay.
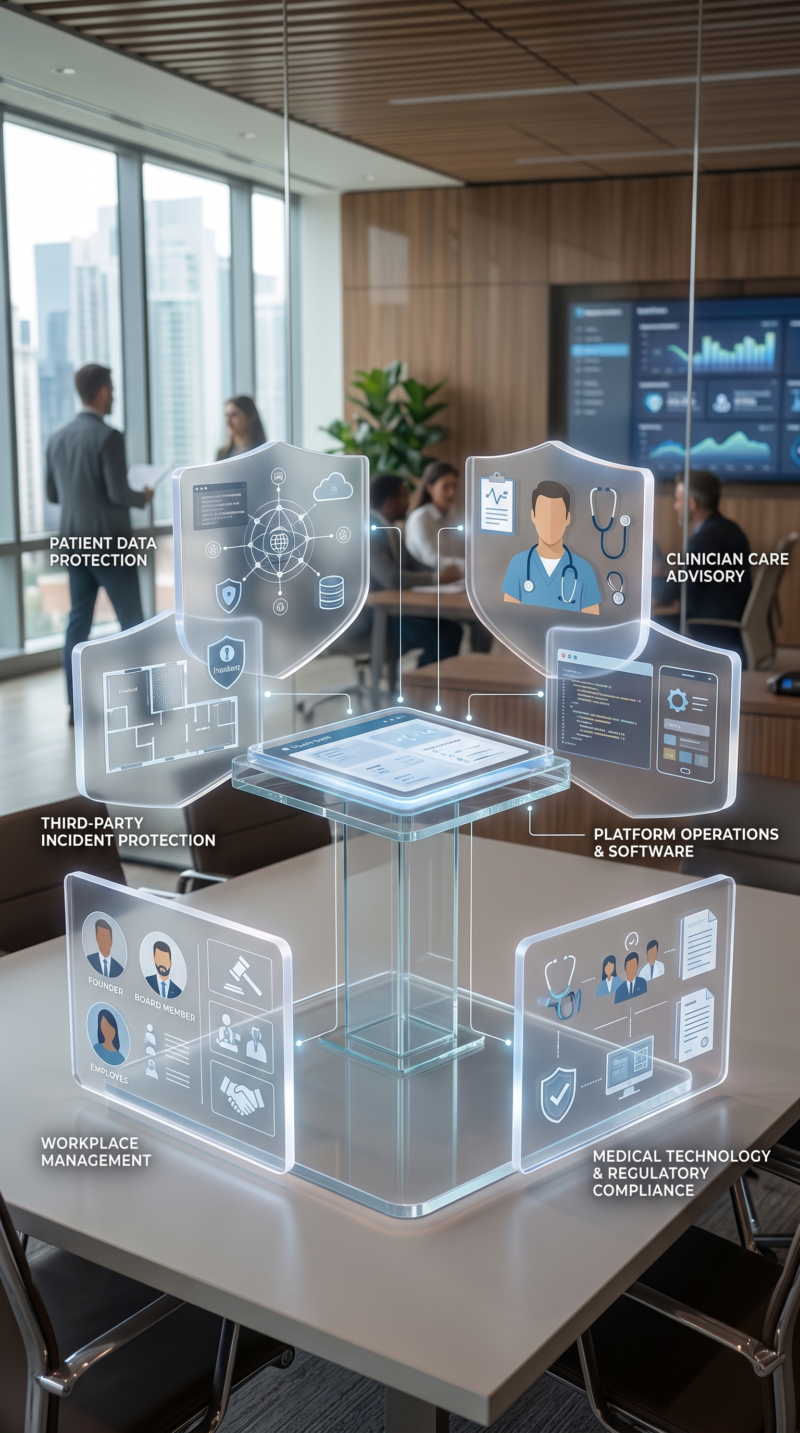
The overlaps are.
Ready to see your real stack, not a generic list? Contact us for a no-obligation review.
Tech E&O vs cyber vs medical malpractice: which policy pays which claim?
They pay for completely different failures, and the dangerous myth is that any one of them covers the others. Tech E&O answers software and service failures. Cyber answers data breaches and privacy events. Medical malpractice answers clinical care by licensed professionals. Assume overlap and you will discover the gap at the worst possible moment, mid-claim.
This is the single most expensive misunderstanding I see in digital health.
Founders think cyber will cover a software defect, or that malpractice will cover the platform, or that one shiny bundled policy handles all three.
Here is the honest map.
Claim scenario |
Cyber |
Tech E&O |
Medical Malpractice |
|---|---|---|---|
|
Hacker steals PHI from your cloud |
Yes |
No |
No |
|
Your app fails to send a critical alert |
No |
Yes |
Maybe (if care) |
|
AI tool gives a wrong clinical recommendation |
No |
Yes (clinical wording) |
Often yes |
|
Clinician negligently misdiagnoses on video |
No |
No |
Yes |
|
Ransomware shuts the platform down |
Yes |
Sometimes (BI) |
No |
|
Defective wearable injures a patient |
No |
No |
No (Product Liability) |
Notice the bottom row.
A defective device is not cyber, not Tech E&O, and not malpractice.
That is why “which policy pays” has to be answered before you buy, not after.
Frankly, if you cannot draw this grid for your own company, you do not yet know whether a better alternative to your current program exists.
Real example from what we see in practice
A tech founder bought a slick online cyber policy with just $50,000 of social engineering fraud coverage, when the real industry standard is around $250,000. Nobody caught it. When the loss hit, there was a $200,000 hole no policy filled, because the platform optimized for speed, not for whether the coverage would actually respond. I audit these programs constantly, and I find a fatal flaw in about 9 out of 10 of them.
How your company structure and clinicians change the coverage
Your legal structure quietly decides who carries which policy, and getting it wrong leaves an entire entity uninsured. Many digital health companies run a PC-MSO structure: a professional corporation that employs the clinicians and a management or technology company that runs the platform. In that setup, malpractice belongs to the clinical entity and cyber plus Tech E&O belong to the platform. Miss the split and a claim finds the uncovered side.
This is where “do we even need malpractice if we don’t employ doctors” gets its real answer.
If independent contractor clinicians deliver care through your platform, their exposure can flow back to you through the contract and through the patient relationship, so you often need coverage or airtight contractual risk transfer regardless of the W-2 question.
Beyond structure, regulation adds the other twist.
That single classification can change your whole digital health company insurance program, which is why we cross-reference this work against our life sciences insurance practice.
Insurance is not a commodity here. The structure is the coverage.
Running a PC-MSO or shipping regulated software? Book a call and we will structure it correctly.
HIPAA, PHI, and what a data breach actually triggers
A breach of protected health information triggers far more than a cleanup bill. It triggers HIPAA breach-notification duties, potential Office for Civil Rights enforcement, ransomware and extortion costs, business interruption, and multi-state notification obligations that scale with your record count. If you handle PHI or act as a business associate (a vendor that handles protected health information for a covered entity under HIPAA), this is not optional coverage. It is the center of your risk.
In practice, most founders underestimate two things here.
First, the size.
That doctor’s office with 5,000 records facing $700,000 in exposure is a small operation; a platform holding hundreds of thousands of records is a different universe.
Breaches affecting 500 or more people must be reported to federal regulators and are posted publicly on the HHS Office for Civil Rights breach portal; in 2024 alone, reported breaches exposed the protected health information of more than 240 million people in the US.
Second, the fine print.
The federal government sets the rules for protected health information and breach notification through HIPAA, and a cheap cyber policy often carries a privacy sublimit or a shared response bucket that is a rounding error once real forensics and legal vendors are engaged.
Size your cyber and privacy coverage to your record counts and your notification footprint, not to the cheapest quote that clears a checkbox.
Want your PHI exposure sized properly? Contact our team.
When do you need it, and what will hospitals, payers, and investors require?
You need each layer at the moment a specific trigger arrives, and the triggers are usually a contract, a patient, or a funding round, not a calendar date. General liability and Tech E&O come early. Cyber becomes urgent the day you touch PHI. Workers comp starts with employees. D&O lands with your first outside capital. Miss the timing and you fail a requirement exactly when a deal is on the line.
A hospital or health system will hand you an insurance requirements exhibit demanding specific limits, additional-insured status (naming them on your policy), and primary-and-noncontributory wording (meaning your coverage pays first, before theirs).
This is the “HIPAA questions are blocking deals” pain, translated into policy terms.
Here is a rough sequencing guide:
That makes your retroactive date and continuous coverage critical.
Let a policy lapse, or start over without a matching retro date, and years of prior work can fall outside coverage.
When you raise, get acquired, or wind down, tail coverage keeps those past acts protected. That last piece is what makes you procurement-ready and financing-ready.
I have seen a $600 online startup package that did not come close to satisfying a single enterprise contract requirement, and enterprise clients routinely require $5 to $10 million in total limits.
Facing a contract or a raise with the wrong limits? Book a call before you sign.
How much does digital health company insurance cost?
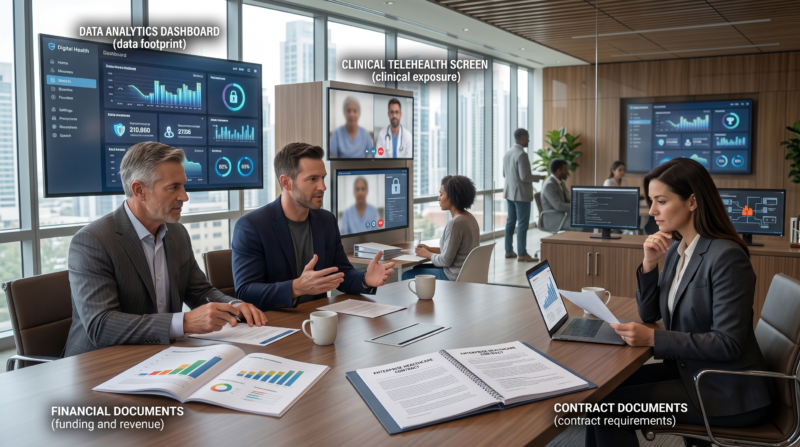
There is no flat price, because premium is driven by what your company actually does, not by your headcount alone. The cost of digital health company insurance moves with how much PHI you hold, whether you deliver clinical care, your funding stage, your revenue, and the limits your contracts demand. Two companies with the same team size can pay very different premiums if one holds a million patient records and the other holds none.
The real drivers underwriters look at are:
What I can tell you is that restructuring a tech client’s program through a specialized broker has saved 30% while closing gaps, because the point was never the cheapest number.
It was the right one.
Want a real quote built on your actual exposures? Contact us.
The Coyle Digital Health Coverage Fit Test
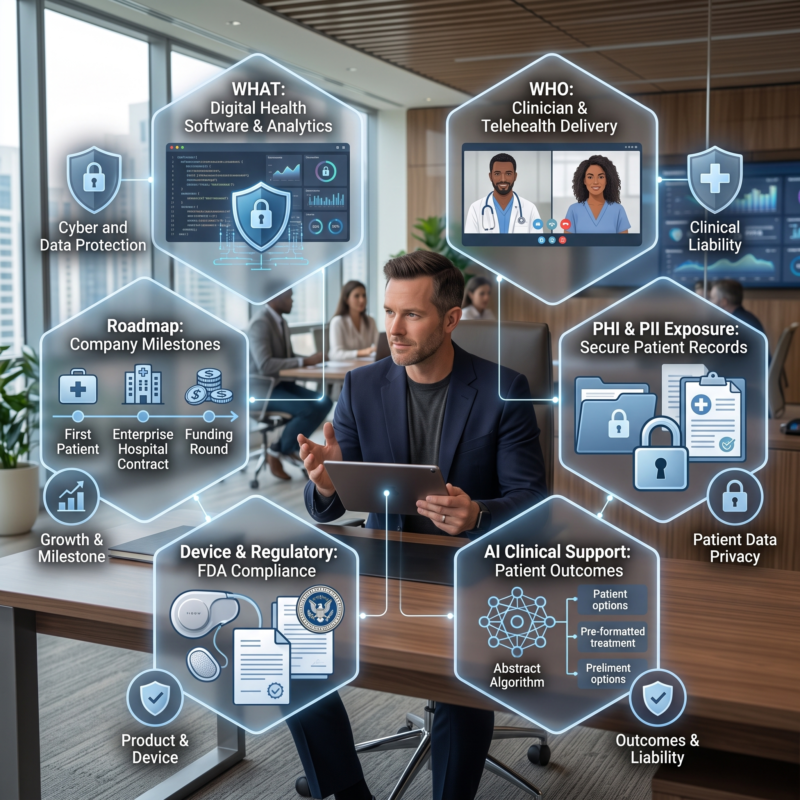
The fastest way to know whether your program fits is to answer six questions, because your honest answers point directly to the policies you need and the ones you do not. This is the framework we use before we structure any digital health program, and it turns an overwhelming market into a short, clear decision.
Run your own company through it:
Two-thirds of repeat founders build insurance into their growth plan early; first-timers usually find out the hard way.
What to know before you buy
Get your digital health company insurance structured correctly
Your company sits at the intersection of healthcare and technology, and that is precisely where generic insurance fails. The stakes are real: a single claim that falls into the gap between your policies can end a company that took years to build. The good news is that once you map your model, your entities, and your contracts, the right program becomes clear and defensible. If you want that done properly, so a claim, a contract, or a raise never becomes a business-threatening problem, let’s have a conversation about your specific exposures.
Book a call with Gordon.
Questions about Digital Health Company Insurance?
Get the Right Coverage for Your digital health company insurance
Most agencies treat a digital health company like ordinary software or an ordinary medical practice, and a claim falls into the gap between the two. We built The Coyle Group to structure the complex risks other agencies can’t, where the policy wording decides whether a claim gets paid.
We build the program around what your company actually does, which entity carries which risk, and what your contracts and investors require. In practice, I find a fatal flaw in about nine out of ten programs I review, and on a digital health account they hide in the fine print.
You shouldn’t find a coverage gap during a breach, an audit, or a funding round. Work with a specialist who reads the policy the way a claim will and closes the gaps first. Let’s talk about your specific exposures.

This article was written by the CEO of The Coyle Group, Gordon B. Coyle, CPCU, ARM, AMIM, PWCA, who has over 40 years of experience working with business owners of all sizes and industries across the US, solving their insurance challenges.
Here’s how to take the next step
Schedule Your Insurance Confidence Assessment
In our 30-minute call, you’ll discover:
Not ready for a call?
Get Free Access to Our Gated Video:
“How to Finally Feel Confident in Your Coverage. “
And discover the exact system we use to help business owners eliminate hidden coverage gaps, stop overpaying, and finally feel confident in their protection.
What Peace of Mind Looks Like
Trusted by business owners across the U.S.
The Coyle Group is 1st class! Gordon and his team are knowledgeable, responsive, and attentive to detail. Gordon is that rare breed of professional who genuinely cares for his clients and works hard to exceed their expectations. I highly recommend them.

The insurance brokerage service was truly tailored to my needs, nothing like those big brokers who steer you toward random policies that don’t fit your profile. Thank you to the team for your help.

I was working with another broker and having difficulty acquiring General Liability coverage. A colleague recommended The Coyle Group. They were able to get coverage bound in just a couple of business days and a policy issued in ten days, and with a solid carrier at a competitive premium. Truly impressive results, plus it was a pleasure working with them. I highly recommend the Coyle Group!

If any business is looking to work with an insurance brokerage firm that is not only excellent at what the firm does, but one that deeply values the needs of the clients, then The Coyle Group is the firm for you. Give them a call and see for yourself. I can assure that you will quickly agree.

Want to know more?
See related blogs
Tech E&O vs. Cyber Insurance: What You Need to Know
Life Sciences – Business Interruption Insurance
Clinical Trial Insurance: What It Covers, What It Costs, and Where the Gaps Are